
What to Expect:
Week 1
October 7
How Organizations Get Exposed
Week 2
October 14
How Organizations Get Breached
Week 3
October 21
What Happens After a Breach
Week 4
October 28
How Organizations Become Resilient
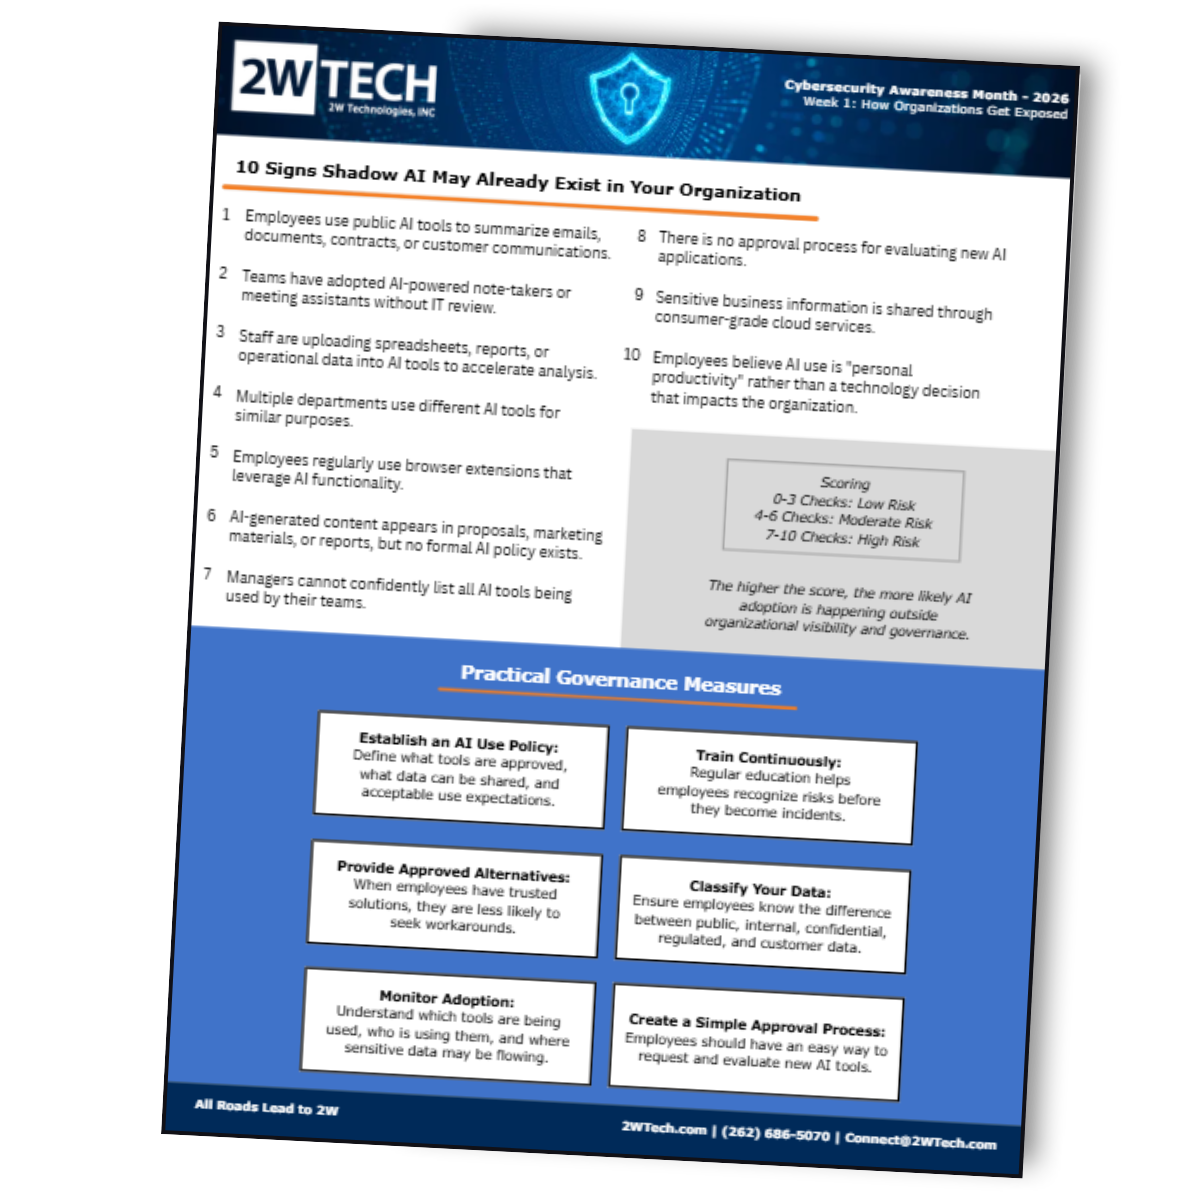
A Snapshot:
The 4 Stages of Cyber Resilience
Understand How Exposure Happens
Most organizations aren’t exposed through sophisticated attacks. They’re exposed through everyday business decisions. Unapproved AI tools, shadow IT, excessive permissions, and a lack of visibility can create risks long before an attacker ever appears.
Reduce Common Attack Paths
Cybercriminals continue to rely on proven tactics because they work. Phishing emails, compromised passwords, missing MFA, and unpatched systems remain some of the most common ways attackers gain access.
Prepare for the First 24 Hours
No organization can eliminate every threat. Resilience starts with having a plan. Response procedures, communication strategies, backups, and recovery processes can dramatically reduce the impact of a cyber incident.
Build Long-Term Resilience
Cybersecurity is no longer just an IT responsibility. Sustainable resilience requires leadership involvement, governance, employee awareness, continuous improvement, and a culture that treats cybersecurity as a business discipline.
8 Traits of a Cyber-Resilient Organization
✓ Visibility into applications, data, and users
✓ Balance innovation with governance
✓ Strong MFA and identity controls
✓ Consistent patching and updates
✓ Tested backups and recovery plans
✓ Leadership incident response readiness
✓ Continuous employee education
✓ Cybersecurity treated as a business discipline
The Latest Insights:
-
Every October, Cybersecurity Awareness Month reminds organizations that security is not a single project. It is a continuous discipline that protects operations, data,...
Read blog
-
Cybersecurity Awareness Month is here, and throughout October we will be focusing on the four stages of cyber resilience. Each stage plays a...
Read blog
-
Artificial intelligence has changed how organizations build software, automate workflows, and solve problems. Tools that generate code or scripts in seconds feel like...
Read blog
Ready to take the next step?